Most business owners think about software security in terms of their servers, their ERP or their online store. Fewer think about the small add-ons their developers install inside their code editor.
This week showed why they should. On October 29, a tampered copy of Anthropic’s Claude Code extension was available in the Cursor editor’s extension marketplace for about 11 hours. Cursor says it reached at most 5,000 users and tried to plant a backdoor on their machines.
What happened in those 11 hours
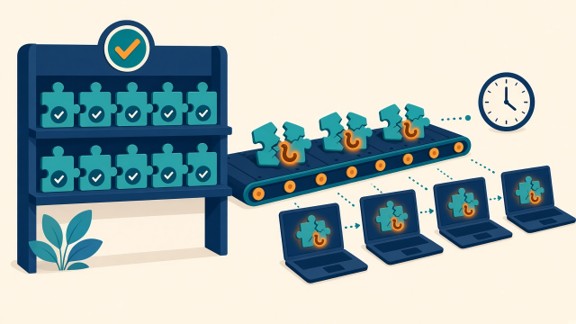
According to Cursor’s security notice, versions 2.1.312 and 2.1.313 for Windows and macOS were live from about 2:27am to 1:35pm Pacific time. Anthropic says it did not build or publish them and that its own systems were not breached. Microsoft confirmed the bad versions never appeared in its Visual Studio Marketplace or on npm.
The extension sent the attacker details about each machine, such as hostname, username, Git email, public IP and the names of environment variables. It added the attacker’s SSH key, set up scripts to keep running, and tried to open a remote tunnel back to the attacker.
The tunnel step usually failed because it needs admin rights. But the key, the persistence scripts and the data upload still went through, and Cursor warns that uninstalling the extension may not remove them.
Two details matter for any business. The tampered version went out under Anthropic’s official account on the marketplace, according to security firm Phorion. And extensions in Cursor update automatically by default. Nobody had to make a bad choice to get infected.
A developer laptop holds more keys than you think
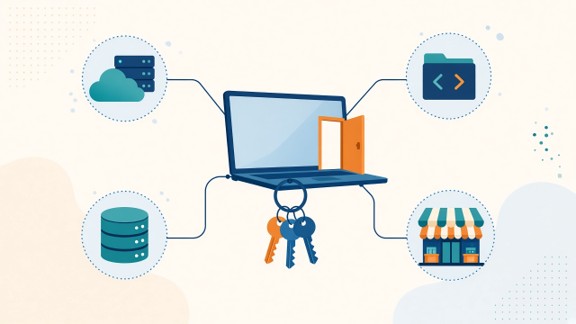
A developer’s machine is rarely just a laptop. It often holds access to your code, your cloud account, your production database and the API keys for services you pay for.
That is why the list of environment variable names is useful to an attacker even without the values. Phorion found the malware sent up to 40 names matching keys, tokens and secrets. It is a map of which doors exist on each machine.
This applies whether you have an in-house team or work with a freelancer or agency. If someone builds or maintains your custom software, their laptop is part of your setup, even if you never see it.
It also fits a wider pattern. Researchers this week disclosed flaws in the built-in browsers of several AI coding tools, and supply-chain attacks on developer packages have been common this year. AI tools run with a lot of access, so a problem inside one travels far.
What to put in place this week
If anyone on your team uses Cursor, check first. Cursor published a script and indicators, and asks affected users to move to version 2.1.314, remove the key and persistence, and rotate credentials reachable from that machine.
Beyond this incident, a few habits make the next one smaller:
- Keep a simple list of which editors, extensions and AI tools your developers use, including contractors.
- Agree on an approved set of extensions, and decide where automatic updates make sense.
- Keep long-lived secrets out of plain environment files on laptops. Prefer short-lived credentials and separate keys for development and production.
- Write down who rotates which keys if one machine is compromised, so you are not figuring it out during an incident.
- Ask your software partner how they handle this. A good one will have a clear answer.
The takeaway
AI coding tools are making development faster, and that is a real benefit. They also run on machines that hold a lot of your business’s access. A trusted name on a marketplace is not a guarantee, so the useful question is how quickly you would know, and how much one laptop could reach.
Does your team know which extensions are installed on the machines that touch your code?
Sources
- Cursor: Security notice on malicious Anthropic.claude-code 2.1.312 and 2.1.313 (Oct 29, 2026)
- The Next Web: Anthropic denies breach as tampered Claude Code extension hits Cursor users (Oct 31, 2026)
- Microsoft Security Blog: Inside a malicious Claude Code-branded extension and its persistent SSH backdoor (Oct 30, 2026)
Threat Frontier: EMBRACE, embedded browser flaws in AI coding tools (Oct 31, 2026)